Practitioner resource
Controls in Microsoft 365, Google Workspace, and GoDaddy You Must Have On Now
November 1, 2026
(212) 561-586024/7: (800) 868-8189
The useful question is whether a control protects the accounts and records the business actually uses. A subscription invoice, an administrator's recollection and a screenshot of a proposed policy answer different questions. Begin with a named owner, an inventory of identities and a record of the current settings. Then establish which protections are enforced, which exceptions remain and what evidence will show that a change worked.
This guide is a verification and implementation-planning sequence, not an instruction to turn every available switch on at once. Identity changes can lock out administrators, stop scanners or interrupt business applications. Preserve relevant settings and logs first if compromise or litigation is suspected. Use an approved change window, a tested recovery path and a person authorized to stop the rollout. Product names and licensing vary; confirm the current tenant rather than assuming another customer's settings apply.
Identify the service and the people who actually control it
Record the Microsoft tenant or Google Workspace organization, primary and secondary domains, subscription editions and responsible administrators. Identify the registrar, DNS host, email platform, reseller, backup provider and security provider separately. A domain registered with GoDaddy may use Microsoft 365, Google Workspace or another email service. Its registrar account is not the same identity as a Microsoft tenant administrator.
Create an access register with one row per privileged role: person, named account, authority, authentication method, recovery owner and last review. Include outside providers and former administrators. Do not place passwords or recovery codes in the register. Confirm that the organization can regain access if its only consultant becomes unavailable. The output is a verified ownership and administration map, not a request to transfer control to a new provider.
Plan strong sign-in protections around business dependencies
Check MFA enrollment and actual enforcement separately. An enrolled user may still access an excluded application or an uncovered account. For Microsoft, determine whether security defaults or a deliberately configured Conditional Access policy set is responsible for protection. These are different approaches. Do not disable a working policy simply to make a dashboard look consistent. Document approved exclusions and the controls that protect them. [MS_ID]
Before enforcement, identify older clients, service identities, applications and equipment that depend on unattended authentication. Pilot the proposed policy with representative users and confirm the administrator recovery procedure. Prefer phishing resistant methods where the service and use case support them. For Google Workspace, inspect the organizational units, groups and enrollment settings that determine enforcement. A policy at the wrong organizational level can leave the intended users unprotected. [GOOGLE_2SV]
Separate administrator work from everyday email
Use identifiable administrative accounts for privileged changes and ordinary accounts for normal correspondence and browsing. Review role assignments against current duties. Remove obsolete privileges through the approved process, while preserving records relevant to a dispute or incident. Treat shared administrator credentials as a gap requiring an accountable replacement rather than assuming that a list of people who know the password is an access record.
Prepare a recovery method that is both protected and usable. Identify who can approve emergency access, where recovery materials are secured and how access will be documented. Google recommends separate administrator and daily accounts and recovery readiness. Test the organizational process without exposing production recovery secrets in a worksheet or email attachment. After a personnel change, verify that recovery addresses and telephone numbers still belong to authorized people. [GOOGLE_ID]
Verify audit logging by producing a known record
Ask an authorized administrator to demonstrate a recent, harmless administrative event in the relevant audit search. Record the event time, search window, service, filters and result. Retain the exported record with its source and collection time. A setting that says auditing is enabled is useful configuration evidence, but a successful sample confirms something different: that the expected activity can be found through the available workflow.
Microsoft's documentation requires customers to verify auditing status and identifies exceptions for some business editions. Audit retention also depends on license, workload and policy. Do not promise that a tenant has a particular number of months of activity merely because another tenant does. For both platforms, record the earliest returned activity, permissions needed to search, export limits and known gaps. Monitoring cannot recover an event that the provider never recorded or no longer retains. [MS_AUDIT] [MS_RETENTION]
Inspect mail forwarding, delegation and application access
Review forwarding at the mailbox, rule, connector and organization levels appropriate to the platform. Identify delegated mailbox access, send permissions, shared mailboxes and third party applications that can read messages or files. Ask the business owner to explain each expected relationship. Preserve suspicious configurations and available activity before changing them during an active matter; the order of containment and evidence collection should follow the incident plan.
Do not assume that a password change removes every route of access. Review sessions, tokens, application grants and recovery settings through the supported administrative process. Document what was revoked, what was left in place and why. A list of permissions shows potential reach; observed activity is needed to support a conclusion about use. Report those two things separately when advising management or counsel.
Check external sharing and ownership of business information
Examine the sharing rules for OneDrive, SharePoint and Teams, or Google Drive and shared drives, according to the organization's actual use. Review representative sensitive repositories, guest access, public or broadly accessible links and externally owned files. Identify the owners who can approve a change. A tenant-wide restriction can affect collaboration, while an exception can preserve unnecessary access if nobody owns its review.
Build a small evidence set for each significant repository: business purpose, owner, sharing setting, membership review and one example showing the effective access. Record whether the example is representative or an exception. Include files linked from messages rather than assuming that preserving a mailbox also preserves every linked document. When employment changes, transfer or preserve business information through an authorized process before deleting accounts or changing licenses.
Distinguish retention, legal holds, archives and backups
Ask what each service is supposed to accomplish. Retention rules govern specified content over time. A legal hold addresses preservation within its supported scope. An archive may preserve an additional copy. A backup is useful only within its actual coverage and recovery capability. None of these labels establishes that all messages, collaboration history, activity logs and linked files are protected.
Have the provider or administrator identify the protected locations, excluded services, retention settings, account dependencies and restore procedure. For a preservation matter, directing counsel determines the relevant scope. For operational recovery, the business sets recovery needs and authorizes a safe restoration exercise. Keep the configuration record and the restoration result separate. A successful restore of one file does not establish that the entire tenant can be recovered within the business's required time.
Secure the GoDaddy account as well as the email tenant
For Microsoft 365 purchased through GoDaddy, verify which administrative tasks are available through the Email and Office dashboard and which require supported Microsoft administration. Record the account owner and the tenant administrator. Protect the GoDaddy account itself, including its recovery details and domain-control permissions. Microsoft's MFA protection for an email account does not by itself secure the registrar or reseller account. [GODADDY]
GoDaddy and Microsoft documentation may describe different rollout details as products change. Use the current workflow for the actual subscription and confirm the effective policy after a change. Do not repeat a universal grace period or advise a customer to disable older controls without checking dependencies. Where the reseller cannot demonstrate a requested capability, obtain a clear explanation of the available edition and escalation path rather than treating an unavailable menu as proof of a security failure.
Establish monitoring, escalation and a record of control ownership
Assign someone to review significant sign-in, administrator, application and sharing events appropriate to the service. Define the events that require immediate escalation and the people who can authorize containment. A notification sent to a former employee or an unattended shared mailbox is not a working response process. Confirm that a representative alert reaches a person with a documented next step.
Maintain a change log linking the business reason, approved configuration, implementation time, operator and verification result. Record exceptions with an owner and review date. Keep rejected proposals and failed changes so the record explains what actually happened. This is more useful during an incident or examination than a policy document that describes controls nobody can demonstrate.
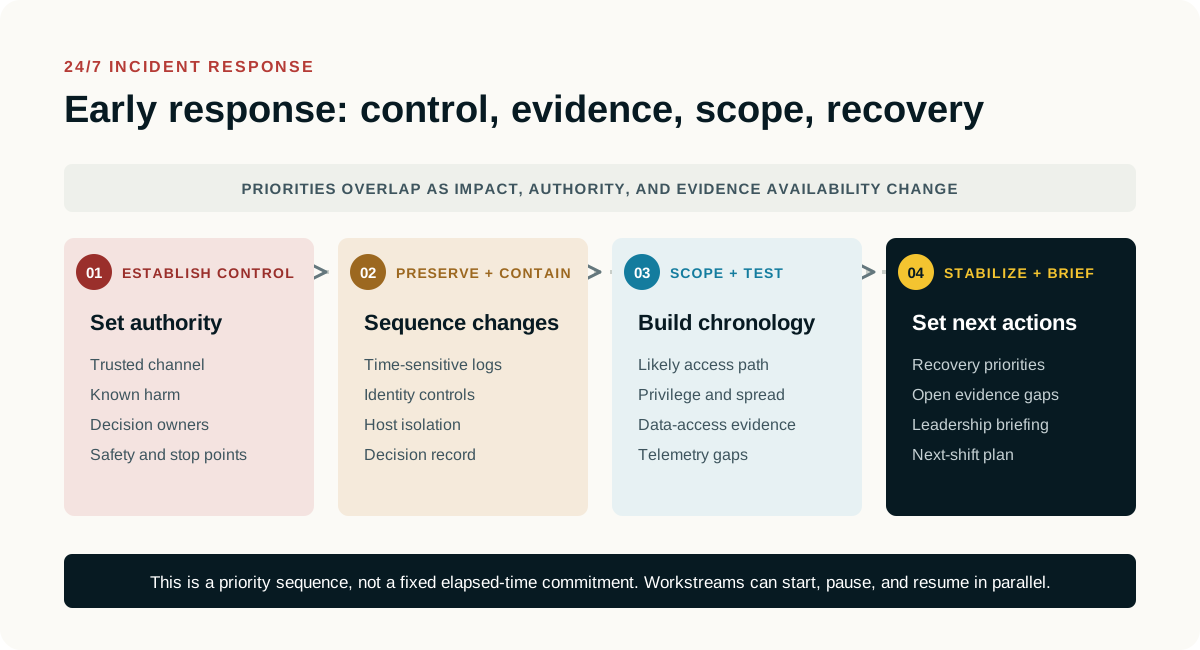
Work through a controlled first-week sequence
On the first day, establish ownership, preserve relevant logs and settings, and identify urgent access risks. Next, verify privileged access, MFA coverage, recovery arrangements and active application grants. Then review representative sharing and retention settings, available audit records and the alert-routing process. Sequence disruptive changes around the business, not around the order of this guide.
Close each action with a named owner, evidence of the effective setting and a remaining-risk statement. Unavailable evidence should remain an open item, not become a green check. If the team discovers suspected compromise, unexplained forwarding, disappearing records or a deadline that is shorter than the available retention, pause the routine review and obtain incident or preservation advice. The objective is an accountable set of controls whose operation can be shown, with a clear record of what still needs attention.
Information Gathering Q&A Checklist
Use this Q&A with the people who own the systems and the relevant legal or business decisions. Mark unknown or not applicable answers explicitly. Record an owner, a confirming source and the date. The public guide-request form asks for your email, not the answers below.
Do not write passwords, recovery keys, unlock codes or authentication secrets here. Record whether authorized access is available, who controls it and how a secure handoff can be arranged. Keep completed copies in the location counsel or the company approves. Do not send a completed record containing sensitive account or employee details through a public contact form.
- Who is directing the matter and who can authorize technical access?
Identify directing counsel, the business decision maker, the IT security owner and any outside administrator. Record the immediate deadline, relevant period and known preservation risk. An employee's possession of a device or an administrator's ability to access an account does not by itself settle the authorized examination scope.
Answer:
Owner, source, date and unresolved questions:
- Who provides the email service and who administers it?
Identify Microsoft 365, Google Workspace, an internal Exchange environment, a hosted service or a combination. Record the tenant or organization reference, relevant domains, mailbox owners, aliases, shared mailboxes and the MSP or administrator responsible. Identify available preservation and export permissions and any licensing question that needs confirmation.
Answer:
Owner, source, date and unresolved questions:
- Does the company have archiving, backups or preservation holds in place?
Name each service and distinguish an archive or journal from a backup, a retention policy and a matter specific hold. Identify what each covers, the available dates, deletion or rotation rules and who can export or restore records. Record whether preservation has actually been verified, rather than treating the existence of a subscription as proof of coverage.
Answer:
Owner, source, date and unresolved questions:
- Does the company supply the computers or do employees use their own?
Record company owned, personally owned, leased and shared equipment separately. Identify the assigned user, operating system, asset or serial reference and present location. Note any employee owned computer used for business and the applicable access agreement. Company ownership and permission to examine particular personal material should not be assumed to be the same.
Answer:
Owner, source, date and unresolved questions:
- Are mobile devices company owned, employee owned or a mixed arrangement?
Identify the phone or tablet, assigned user, model and operating system where known, and who currently holds it. Distinguish the owner of the handset from the owner of the cellular service account. Record whether work data is separated into a managed profile and whether a replacement, return or wipe is already scheduled.
Answer:
Owner, source, date and unresolved questions:
- Whose Apple, Google or Samsung account is registered or signed in on each phone?
Record each relevant account as personal, company controlled or unknown, and identify who can lawfully arrange access. For Apple devices, note any organization enrollment and known Activation Lock status separately from the signed in Apple Account. For Android devices, distinguish personal and work profiles and note relevant Google and Samsung accounts separately. Do not sign out or reset an account to answer this question. [S14] [S15]
Answer:
Owner, source, date and unresolved questions:
- Does the company use MDM and what does it actually manage on these devices?
Name the management service, administrator and enrollment mode, including supervision or work profile details where applicable. Record the last known device contact and any pending retire, lock or wipe command. A device appearing in a management console does not establish access to every personal application, message or backup. Preserve the management record without issuing a command merely to test capability.
Answer:
Owner, source, date and unresolved questions:
- Can the company recover the BitLocker or other encryption keys for each relevant computer?
Ask whether recovery material is actually available for the identified device and drive, where it is escrowed and who has authorized retrieval permission. Possible locations include Microsoft Entra ID, Active Directory or another approved store. Note FileVault or other encryption separately. Do not assume that MDM enrollment guarantees key availability, and do not place the key itself on this record. [S13]
Answer:
Owner, source, date and unresolved questions:
- Who controls identity, administrator access and multifactor authentication?
Identify the identity provider, relevant privileged accounts, outside administrator and person who can approve an export or collection. Note access dependencies such as an unavailable administrator or authentication device without recording secrets. Shared or delegated access should be identified because account activity may require additional evidence before it can be attributed to an individual.
Answer:
Owner, source, date and unresolved questions:
- Which cloud storage, collaboration and messaging services contain relevant work?
Identify shared drives, Teams, SharePoint, OneDrive, Slack, Google Chat and other platforms actually used for the relevant work. Note external ownership, linked documents, personal accounts used for business and any unsupported or unavailable source. A mailbox export should not be assumed to include the contents of every linked file or separate conversation.
Answer:
Owner, source, date and unresolved questions:
- What activity logs and endpoint records are available now?
Ask the responsible administrator which email, identity, endpoint, cloud sharing, USB, security and data protection records exist for the relevant period. Record actual date coverage, export permissions, known gaps and the next expiration or rotation point. Enabling a logging feature today should not be described as recovering activity that was never recorded.
Answer:
Owner, source, date and unresolved questions:
- What has already changed on the devices or accounts?
Record password resets, access restrictions, account deletions, mailbox conversions, software installations, cleanup activity, repairs, cloud sync changes and any device reset or wipe. Identify who acted, when and why. Include informal handling or earlier collections so the examiner can distinguish relevant historical activity from changes made during the response.
Answer:
Owner, source, date and unresolved questions:
- Which tenant, edition, reseller and DNS owner are involved?
Identify the actual platform and authorized administrators before using a product checklist.
Answer:
Owner, source, date and unresolved questions:
- Which applications, service identities or devices could be affected by an identity-control change?
Record dependencies, approved exceptions, recovery arrangements and a change owner.
Answer:
Owner, source, date and unresolved questions:
Primary sources and further reading
Prepared November 1, 2026. Sources explain the general framework; applicability, licenses, available records and legal requirements vary. This guide is technical preparation, not legal advice or an assurance of compliance or admissibility.
- MS_ID: Microsoft Entra security defaults
- MS_AUDIT: Microsoft Purview: turn auditing on or off
- MS_RETENTION: Microsoft audit log retention policies
- GOOGLE_ID: Google Workspace security best practices for administrators
- GOOGLE_2SV: Google Workspace: deploy 2-Step Verification
- GODADDY: GoDaddy Microsoft 365 security defaults
- S13: Microsoft BitLocker recovery overview
- S14: Apple guidance on Activation Lock and device management
- S15: Android Enterprise guidance on work profiles