Incident scope and loss chronology
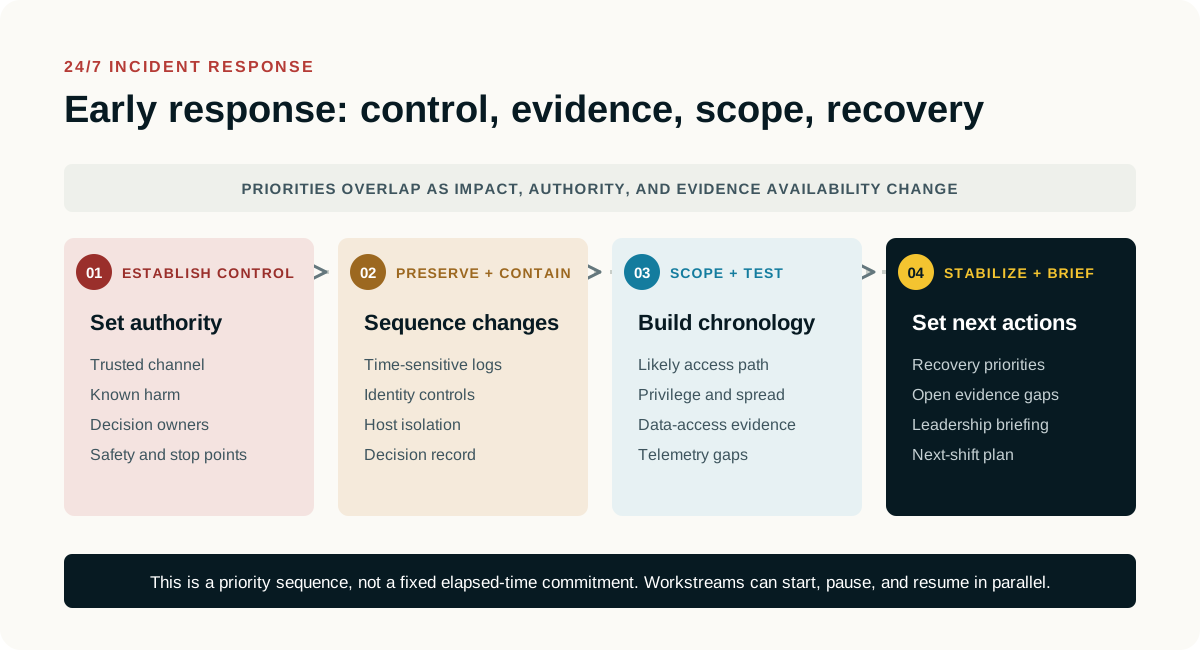
- 24/7 cyber incident response
Document the event, containment actions and recovery sequence.
- Email and Microsoft 365 forensics
Examine payment threads and compromised mailbox activity.
- Cloud and SaaS forensics
Identify supported cloud-access and data-transfer facts.
- Digital forensics and analysis
Correlate device activity with the reported loss.