Practitioner resource
The NYDFS 23 NYCRR Part 500 Technical Evidence Playbook
November 1, 2026
(212) 561-586024/7: (800) 868-8189
An examination response is easier to defend when the entity can connect a regulatory requirement to a named owner, the systems within scope, the control that operates there and evidence showing what happened during the relevant period. A policy binder alone cannot establish that an account was removed, a backup restored or an incident evaluated on time. Equally, a dashboard warning does not establish a legal violation without understanding its scope and context.
This playbook helps a covered entity assemble and explain technical evidence for counsel, compliance leaders, internal audit and authorized examiners. It is not a certification of compliance or a substitute for the regulation. Determine the entity's obligations, exemptions and reporting requirements with the appropriate legal and compliance owners. Keep factual exceptions visible and distinguish current remediation from the state of controls during the period under review.
Establish the covered entity, examination period and applicable requirements
Begin with the legal entity and its relevant license, registration or other DFS authorization. Identify affiliates, shared services and providers that operate systems on its behalf. Record the examination period, the request or notice received and the person coordinating the response. Confirm whether a claimed exemption is current, documented and relevant to each requirement rather than treating the word exempt as a complete answer.
Use the official regulation and current DFS guidance to build the requirements register. Mark the basis for each applicability decision and preserve the approving person's record. Do not treat every organization that does business in New York as a Part 500 covered entity. Conversely, another regulator's oversight does not by itself settle the entity's DFS obligations. The applicable rule and entity circumstances control. [DFS_FAQ]
Create one evidence index with a clear chain to each assertion
Give each requirement or examination request a stable reference. For each response, identify the control owner, relevant systems, period, evidence source, collection date and location. Use a short explanation of what the evidence demonstrates and what it does not. For example, a configuration export shows a setting at a point in time, while activity records may help demonstrate operation over a period.
Keep original exports separate from annotated presentation copies. Preserve the query, filters, source time zone, export options and errors. If the source is a provider portal, record the tenant and administrative scope used. A result generated today may not demonstrate the historical state requested by an examiner. Identify historical gaps early and seek other authorized records without changing timestamps or rewriting the earlier account.
Make the risk assessment traceable to actual business risk
Use the risk assessment to explain why particular assets, access routes and business processes matter. Connect identified risks to their control owners and supporting evidence. A repeated list of generic threats does not show how the entity evaluated its own environment. Keep the assessment's scope, assumptions, methodology, risk criteria and material exclusions with its findings.
DFS's September 2026 guidance emphasizes an assessment tailored to the entity, documented risks, traceability to controls and updates when circumstances change. Use that guidance alongside the regulation, not as a replacement for it. Record management's remediation or risk-acceptance decisions and the facts on which they relied. A later reassessment should explain what changed rather than overwrite the earlier result. [DFS_RISK]
Reconcile inventories with systems and data that actually exist
Compare the asset inventory with representative identity, endpoint, cloud, network and business-application records. Identify owners, locations and significant dependencies. Include systems supplied through shared services and the information the entity needs from providers to understand them. Keep unmatched assets and undocumented owners as open items with an accountable next step.
An inventory can support an examination only within its demonstrated coverage. A spreadsheet of purchased laptops may omit virtual machines, tenant applications or infrastructure operated by a provider. A discovery tool may miss offline or isolated systems. Document the collection methods and reconciliation process. The objective is an explainable inventory whose limitations are understood, rather than an unsupported statement that a single export contains everything.
Show how access is approved, reviewed and removed
Assemble evidence of account creation, privilege approval, periodic review and termination. Include ordinary users, privileged administrators, service identities, remote access and relevant provider access. Review a sample of actual personnel changes against the corresponding access records. Explain discrepancies with facts: a delayed disablement, an account used by a service or an approval that could not be located.
For MFA, distinguish the written policy, configured scope and effective enforcement. Preserve policy exports, exclusions, alternative-control decisions where applicable and representative operating records. Identify the systems and people that the evidence actually covers. A successful MFA event for one administrator is not proof that every user and application is protected. The staged requirements through November 2025 are already in the past as of this edition; do not present them as a future implementation window. [DFS_TIMELINE]
Connect vulnerability findings to remediation and retesting
Keep the approved scope, asset coverage, assessment dates and material exclusions with penetration-test and vulnerability-assessment reports. Reconcile findings to responsible owners, remediation decisions, target dates and evidence of closure. Where a weakness was accepted or a fix deferred, retain the rationale and applicable compensating measures rather than quietly deleting the finding from a dashboard.
Show the distinction between an automated result, a validated weakness and a retest observation. A rescan can help determine whether a particular issue remains detectable under the retest conditions. It does not establish the absence of every attack path or prove the entire environment secure. If material systems were excluded, explain who authorized that boundary and what other evidence addresses the risk. Testing should support the entity's risk decisions and examination response, not substitute for them.
Explain logging, monitoring and the limits of historical coverage
For important sources, record the enabled events, collection path, retention, time synchronization and responsible monitoring team. Identify whether records are provider generated, forwarded to another platform or stored locally. Preserve evidence that alerts were received and handled where the examination concerns monitoring operation, not merely the existence of a product license.
Build a coverage table for the review period. Mark earliest and latest available records, known interruptions and relevant changes to settings or licenses. Treat missing logs as a limit on the account, not proof that nothing happened. Where the entity relies on a provider, request the specific evidence needed and retain the provider's stated coverage and exceptions. Avoid inserting personal information into a broad response package when a suitably scoped or redacted record will address the request.
Demonstrate recovery through actual exercise records
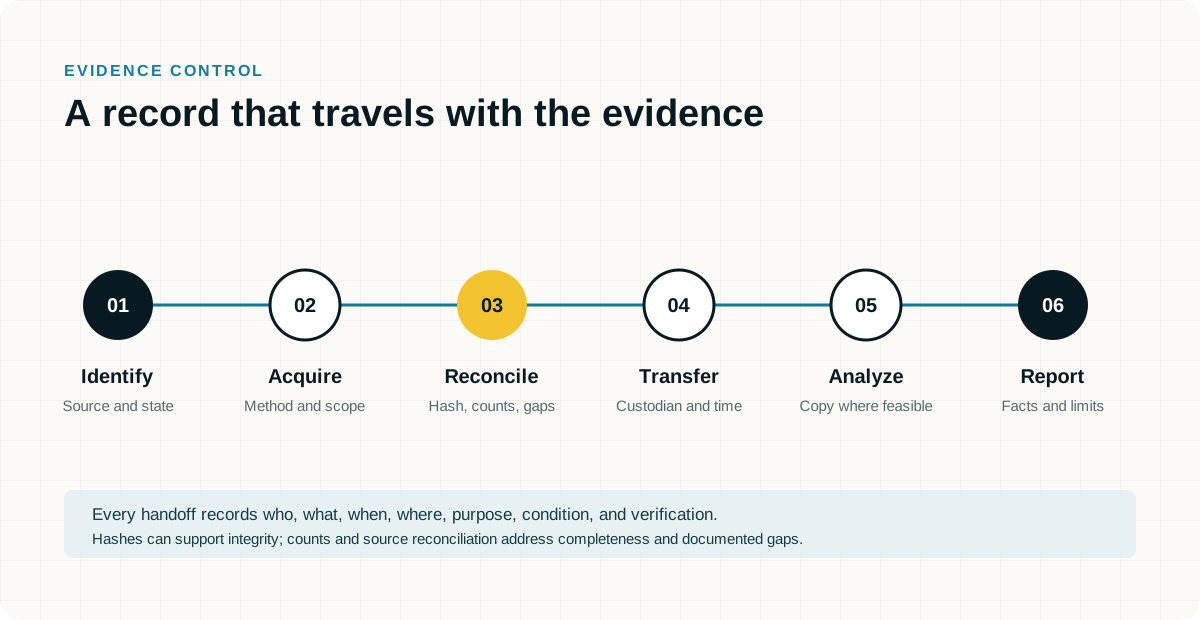
Collect the incident-response and business-continuity or disaster-recovery plans applicable to the reviewed systems. Identify the people responsible for using them, the exercises performed and the resulting corrective actions. For restoration evidence, distinguish a backup job's reported completion from an observed recovery of the required data or system.
Preserve the exercise scenario, participants, start and finish times, dependencies, exceptions and decisions. If the exercise was limited to a sample or an isolated environment, say so. Record how unresolved findings were assigned and followed through. A polished report that omits a failed restoration step is less useful than a complete account that shows the failure, its consequence and the remediation. [DFS]
Address third parties and shared responsibility directly
List the providers relevant to each request and identify the business owner responsible for the relationship. Match the entity's claimed control to the contract, available assurance material and any direct operating evidence. Read the scope, period and exceptions in provider reports rather than treating the report's existence as confirmation of every service the entity uses.
Where responsibilities are divided, document who approves access, enables logging, preserves evidence and responds to an incident. A provider may operate infrastructure while the entity remains responsible for tenant settings or user access. Keep unanswered requests visible. If a provider cannot supply historical evidence, describe the gap and identify possible alternative records. Do not represent an assurance letter as a substitute for facts the letter does not address.
Preserve the incident and notification decision record
Maintain a chronology separating initial detection, escalation, determination, containment, evidence collection and notifications. The regulation's incident-notice provisions and its defined terms require careful application. Record who made the relevant determination, the facts known at that point and the time of each submission or update. Do not use a general internal severity label as a substitute for the applicable regulatory analysis.
Part 500 also contains distinct provisions for extortion-payment notices and explanations. Keep payment-related decisions under the direction of authorized leadership and counsel. This guide does not authorize payment or determine notification duties. Technical personnel should preserve the factual account and identify changing information promptly, without promising that an early triage review can establish the full scope of access. [DFS]
Support the annual submission with the record it actually requires
Identify the data and documentation supporting the entity's annual submission and the responsible signatories. Distinguish a current improvement project from evidence about the prior calendar year. The regulation provides different submission paths, including certification of material compliance and acknowledgment of noncompliance. Counsel and responsible officers determine the appropriate submission, not the presence of a completed checklist.
Keep the supporting records and known areas requiring improvement together with remediation plans and their status. Preserve versions and approvals so the entity can explain the account later. Do not label a missing record compliant merely because its owner expects to find it. A technical specialist can help reconcile evidence and articulate limitations; that work does not replace the signatories' responsibilities. [DFS]
Deliver a response package that a reviewer can follow
Prepare a concise response narrative and link it to the indexed supporting records. Use consistent entity names, system identifiers, dates and evidence references. Separate facts, interpretations and open questions. Identify documents supplied by a provider and statements based only on an interview. Make the source and limits visible without flooding the reviewer with unrelated exports.
Before delivery, have the control owner confirm factual accuracy and have counsel or compliance review the response within their responsibilities. Test whether a person unfamiliar with the project can follow a material assertion to its support. Resolve broken references, conflicting dates and unexplained gaps. Preserve the delivered version and the record of later corrections. That produces an examination response whose reasoning can be checked, even when the underlying environment still contains work to do.
Information Gathering Q&A Checklist
Use this Q&A with the people who own the systems and the relevant legal or business decisions. Mark unknown or not applicable answers explicitly. Record an owner, a confirming source and the date. The public guide-request form asks for your email, not the answers below.
Do not write passwords, recovery keys, unlock codes or authentication secrets here. Record whether authorized access is available, who controls it and how a secure handoff can be arranged. Keep completed copies in the location counsel or the company approves. Do not send a completed record containing sensitive account or employee details through a public contact form.
- Who is directing the matter and who can authorize technical access?
Identify directing counsel, the business decision maker, the IT security owner and any outside administrator. Record the immediate deadline, relevant period and known preservation risk. An employee's possession of a device or an administrator's ability to access an account does not by itself settle the authorized examination scope.
Answer:
Owner, source, date and unresolved questions:
- Who provides the email service and who administers it?
Identify Microsoft 365, Google Workspace, an internal Exchange environment, a hosted service or a combination. Record the tenant or organization reference, relevant domains, mailbox owners, aliases, shared mailboxes and the MSP or administrator responsible. Identify available preservation and export permissions and any licensing question that needs confirmation.
Answer:
Owner, source, date and unresolved questions:
- Does the company have archiving, backups or preservation holds in place?
Name each service and distinguish an archive or journal from a backup, a retention policy and a matter specific hold. Identify what each covers, the available dates, deletion or rotation rules and who can export or restore records. Record whether preservation has actually been verified, rather than treating the existence of a subscription as proof of coverage.
Answer:
Owner, source, date and unresolved questions:
- Does the company supply the computers or do employees use their own?
Record company owned, personally owned, leased and shared equipment separately. Identify the assigned user, operating system, asset or serial reference and present location. Note any employee owned computer used for business and the applicable access agreement. Company ownership and permission to examine particular personal material should not be assumed to be the same.
Answer:
Owner, source, date and unresolved questions:
- Are mobile devices company owned, employee owned or a mixed arrangement?
Identify the phone or tablet, assigned user, model and operating system where known, and who currently holds it. Distinguish the owner of the handset from the owner of the cellular service account. Record whether work data is separated into a managed profile and whether a replacement, return or wipe is already scheduled.
Answer:
Owner, source, date and unresolved questions:
- Whose Apple, Google or Samsung account is registered or signed in on each phone?
Record each relevant account as personal, company controlled or unknown, and identify who can lawfully arrange access. For Apple devices, note any organization enrollment and known Activation Lock status separately from the signed in Apple Account. For Android devices, distinguish personal and work profiles and note relevant Google and Samsung accounts separately. Do not sign out or reset an account to answer this question. [S14] [S15]
Answer:
Owner, source, date and unresolved questions:
- Does the company use MDM and what does it actually manage on these devices?
Name the management service, administrator and enrollment mode, including supervision or work profile details where applicable. Record the last known device contact and any pending retire, lock or wipe command. A device appearing in a management console does not establish access to every personal application, message or backup. Preserve the management record without issuing a command merely to test capability.
Answer:
Owner, source, date and unresolved questions:
- Can the company recover the BitLocker or other encryption keys for each relevant computer?
Ask whether recovery material is actually available for the identified device and drive, where it is escrowed and who has authorized retrieval permission. Possible locations include Microsoft Entra ID, Active Directory or another approved store. Note FileVault or other encryption separately. Do not assume that MDM enrollment guarantees key availability, and do not place the key itself on this record. [S13]
Answer:
Owner, source, date and unresolved questions:
- Who controls identity, administrator access and multifactor authentication?
Identify the identity provider, relevant privileged accounts, outside administrator and person who can approve an export or collection. Note access dependencies such as an unavailable administrator or authentication device without recording secrets. Shared or delegated access should be identified because account activity may require additional evidence before it can be attributed to an individual.
Answer:
Owner, source, date and unresolved questions:
- Which cloud storage, collaboration and messaging services contain relevant work?
Identify shared drives, Teams, SharePoint, OneDrive, Slack, Google Chat and other platforms actually used for the relevant work. Note external ownership, linked documents, personal accounts used for business and any unsupported or unavailable source. A mailbox export should not be assumed to include the contents of every linked file or separate conversation.
Answer:
Owner, source, date and unresolved questions:
- What activity logs and endpoint records are available now?
Ask the responsible administrator which email, identity, endpoint, cloud sharing, USB, security and data protection records exist for the relevant period. Record actual date coverage, export permissions, known gaps and the next expiration or rotation point. Enabling a logging feature today should not be described as recovering activity that was never recorded.
Answer:
Owner, source, date and unresolved questions:
- What has already changed on the devices or accounts?
Record password resets, access restrictions, account deletions, mailbox conversions, software installations, cleanup activity, repairs, cloud sync changes and any device reset or wipe. Identify who acted, when and why. Include informal handling or earlier collections so the examiner can distinguish relevant historical activity from changes made during the response.
Answer:
Owner, source, date and unresolved questions:
- Which covered entity, review period and examination requests are in scope?
Identify the applicability and exemption decision owner.
Answer:
Owner, source, date and unresolved questions:
- Which control assertions lack current or historical supporting records?
Assign an owner, source request and response date rather than marking the gap complete.
Answer:
Owner, source, date and unresolved questions:
Primary sources and further reading
Prepared November 1, 2026. Sources explain the general framework; applicability, licenses, available records and legal requirements vary. This guide is technical preparation, not legal advice or an assurance of compliance or admissibility.
- DFS: NYDFS Cybersecurity Regulation, 23 NYCRR Part 500
- DFS_RISK: NYDFS September 10, 2026 risk assessment guidance
- DFS_FAQ: NYDFS Cybersecurity FAQs
- DFS_TIMELINE: NYDFS implementation timeline for covered entities
- S13: Microsoft BitLocker recovery overview
- S14: Apple guidance on Activation Lock and device management
- S15: Android Enterprise guidance on work profiles