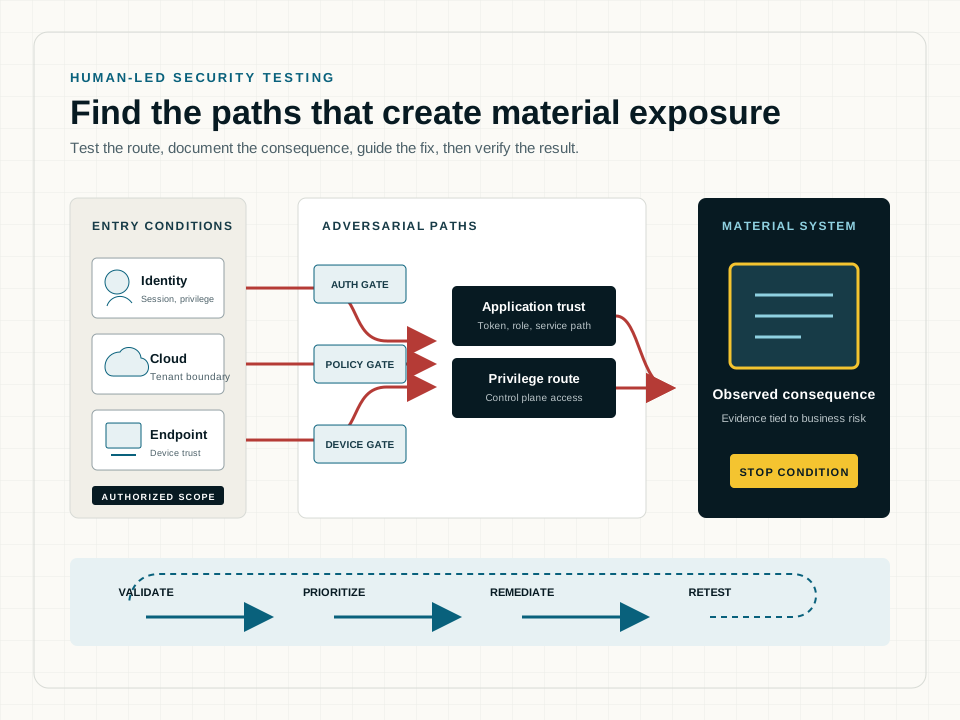
A vulnerability scan lists conditions. Human-led penetration testing asks whether those conditions can be combined into adversarial attack paths that reach a material asset. GDF defines rules of engagement, tests within approved boundaries, limits operational risk, and provides evidence that engineering teams can reproduce.

Human-led testing. AI-augmented analysis.
AI helps our testers map exposed assets, identify potential weaknesses and correlate findings into attack paths worth testing. Human testers decide what to pursue, validate the evidence and explain the business impact within your authorized scope.
When source-code access is included in the engagement, AI-assisted code review helps examine authentication, authorization, data handling and application logic. Our testers review the relevant code, assess suspected weaknesses in context and, where permitted, test whether they can be exploited in the running application. The report distinguishes confirmed findings from issues that still need validation.
Your team receives reproducible evidence and prioritized remediation advice. Code access, tool use and handling of proprietary material are agreed before testing begins.
Rules of engagement with real operating limits
Scope identifies target ranges, domains, applications, identities, cloud subscriptions, third parties, prohibited actions, testing windows, escalation contacts, and stop conditions. Production systems may require lower-impact techniques or coordinated validation. The plan also covers test accounts, source addresses, data handling, and emergency communications.
Attack paths, not isolated screenshots
Testers examine discovery, authentication, authorization, session control, privilege boundaries, exposed services, trust relationships, cloud roles, secrets, segmentation, and application logic. Exploitation is limited to the approved evidence needed to demonstrate consequence. Client data is not copied merely to make a point, and any test data handling is defined in the rules of engagement.
- External and internal network penetration testing
- Web application, API, mobile-backend, and business-logic testing
- Microsoft 365, Entra ID, AWS, Azure, and cloud control testing
- Wireless, remote access, and segmentation validation
- Retest evidence tied to the original finding
A remediation record engineers can close
Each finding identifies the prerequisite, demonstrated path, affected scope, business consequence, evidence, and a prioritized fix. Vulnerability remediation guidance considers compensating controls and operational constraints. A retest checks the original route and agreed adjacent conditions at a stated date. It records residual risk and untested paths rather than declaring the wider environment closed or secure.