GDF helps utilities and service providers collect, test, and organize technical records for NERC CIP requirements that the applicable Registered Entity has placed in scope. Applicability depends on registration, NERC function, Bulk Electric System responsibilities, asset and system categorization, the governing standard and requirement version, implementation dates, and the review period. The Registered Entity, compliance team, Regional Entity, and counsel retain applicability, interpretation, attestation, and submission decisions. GDF does not provide a legal compliance opinion.
A record from requirement to source
The evidence map records the Responsible Entity or Registered Entity designation used by the client, relevant NERC function, Regional Entity, Bulk Electric System Cyber System categorization, standard and requirement identifier, version and effective date, audit or review period, control owner, covered population, source system, collection method, reviewer, exception path, and retention location. Screenshots can support a record, but repeatable exports and configuration data generally provide stronger coverage and allow reconciliation.
Approved future standards or requirement revisions are tracked separately from provisions in force during the review period. A readiness review for a future enforcement date is labeled as readiness work and is not presented as evidence that a current requirement applies or has been satisfied.
Validation under OT constraints
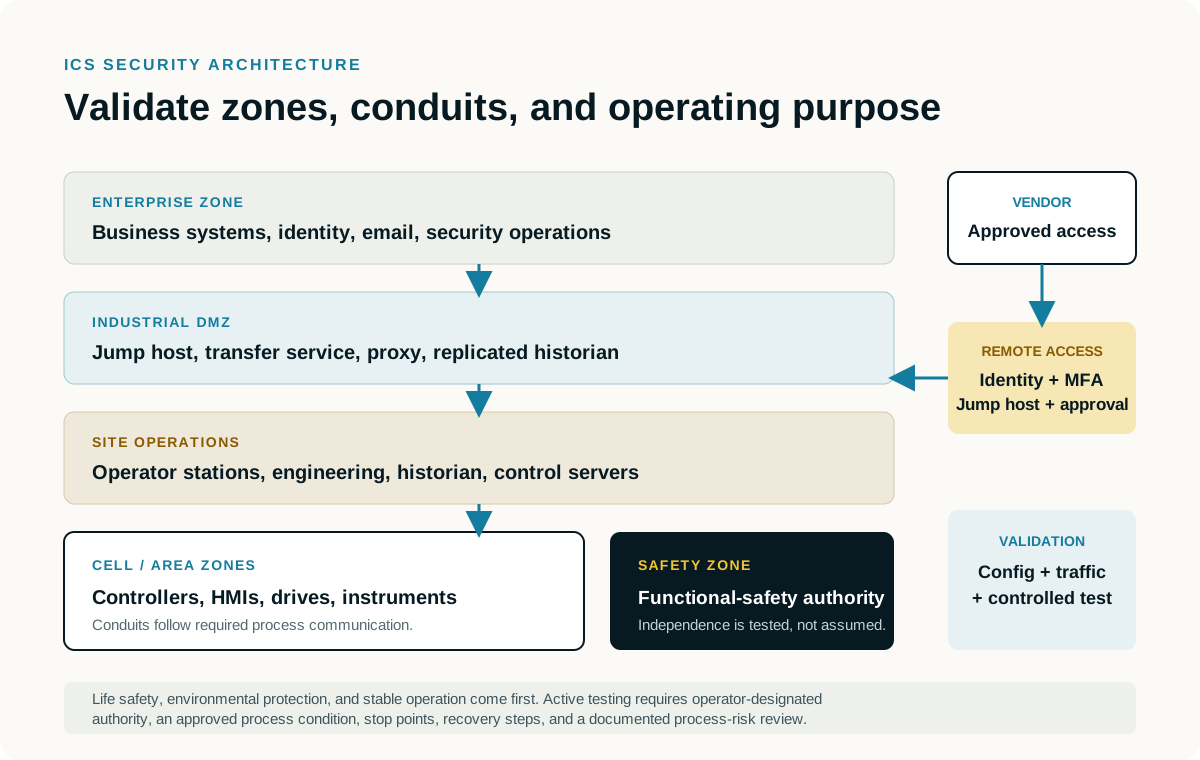
Testing accounts for life safety, environmental protection, stable operation, system availability, change restrictions, vendor support, protected cyber assets, and operator-designated authority. Active methods require an approved process condition, stop points, and recovery steps. Passive review and configuration analysis are used where active methods could create risk. Exceptions, excluded assets, inaccessible sources, and untested controls are recorded rather than treated as passed controls.
- Asset and scope reconciliation
- Electronic security perimeter and remote-access evidence
- Identity, privilege, account review, and termination records
- Vulnerability, patch, change, configuration, and exception evidence
- Incident, backup, recovery, exercise, and corrective-action records
Audit support without replacing accountable roles
GDF can collect, test, organize, and explain technical records for the scope and period supplied by the client. Registered Entities, Responsible Entity control owners, compliance teams, internal audit, and counsel retain their responsibilities for applicability, interpretation, attestation, submission, and representation to a Regional Entity, NERC, regulator, or auditor.