Organizations subject to 23 NYCRR Part 500 need more than policy language. GDF supports security and compliance teams with technical evidence concerning asset inventory, risk assessment, vulnerability management, penetration testing, access control, logging, incident response, and recovery. Counsel determines regulatory interpretation and reporting obligations.
Control claims mapped to observable records
A test plan identifies the policy statement, system owner, technical implementation, evidence source, population, sample, expected result, exception path, and retest method. Evidence may include configuration exports, identity records, scan coverage, tickets, approvals, log-retention settings, exercise records, backup tests, and dated correction and retest records.
The work is designed to coexist with internal audit, outside counsel, and existing governance platforms. GDF does not issue a legal compliance opinion or certification.
Security testing with an evidence trail
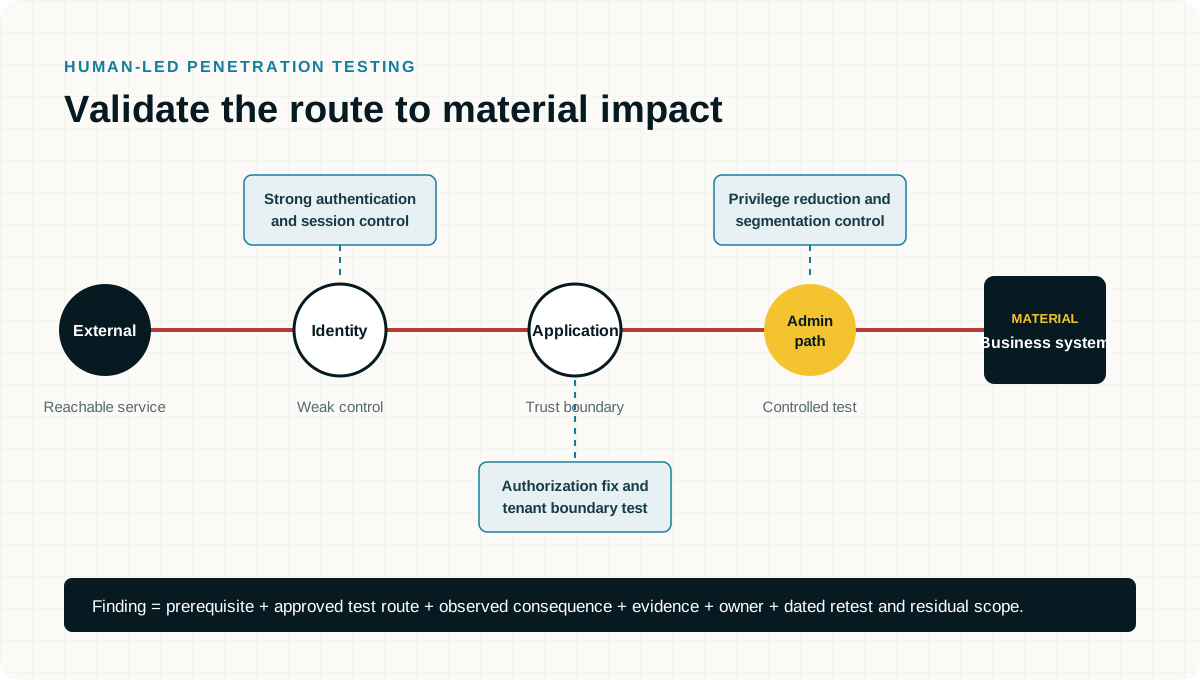
Penetration testing and vulnerability assessment can be aligned with covered assets and material risk. Coverage is reconciled against inventories and documented exclusions. Material findings are tracked through vulnerability remediation guidance, owner response, exception approval, and technical retest.
- Asset and scope reconciliation
- Penetration-test and vulnerability-program evidence
- Privileged access and identity-control validation
- Logging, monitoring, retention, and response record review
- Remediation and exception evidence packages
Support for incidents and annual review
During a cyber event, responders preserve the chronology, affected systems, containment decisions, data-access facts, and corrective actions that leadership and counsel may need. Between events, incident readiness planning tests whether contacts, logs, backups, and decision paths work as documented.